Avoid a Provider Null Route: 4 DDoS Layers VPS Operators Need
Avoid a Provider Null Route: 4 DDoS Layers VPS Operators Need
Protecting a VPS against DDoS requires four layers: provider/edge mitigation, network/protocol controls, application-layer defenses, and continuous detection with an incident playbook. Skip any one of them and an attacker finds the gap. Expect your host to fall back on null-routing once traffic crosses a threshold, cutting your server off the internet entirely, unless you’ve paid for scrubbing, which filters bad traffic while keeping you online.
TL;DR:
- Providers typically use null-routing or scrubbing centers, with the latter offering filtered traffic and better uptime during high-volume attacks.
- On-host configurations like SYN cookies and connection limits help buy time but cannot prevent volumetric Layer 3 floods without provider-level mitigation.
- Layer 7 attacks require application-layer defenses such as CDNs and WAF rules, since they mimic legitimate traffic and are harder to block at the network level.
- For critical workloads, it is essential to understand provider thresholds, scrubbing options, and request forensic reports to prepare an effective incident response.
- Null-routing is suitable only for low-stakes projects, while paid scrubbing and detailed telemetry are necessary for real-time, sustained DDoS protection.
Table of Contents
- What Are the VPS DDoS Layers, and Which Attacks Hit Each One?
- How Do Providers Actually Mitigate DDoS Attacks?
- What VPS Settings Reduce DDoS Damage at the Network Level?
- How Do You Stop Layer 7 DDoS Attacks on a VPS?
- How Should You Monitor and Respond to a DDoS Attack?
- What Should You Do the Moment Your VPS Comes Under Attack?
- How AceRDP Approaches Layered DDoS Protection
- When Does Null-Routing Make Sense Versus Paying for Scrubbing?
- Get DDoS-Protected VPS Hosting Built for Performance
- Sources
- FAQ
What Are the VPS DDoS Layers, and Which Attacks Hit Each One?
Every DDoS attack targets a specific point in the network stack, and the fix depends entirely on which point that is. Confusing a Layer 7 request flood with a Layer 3 bandwidth flood, and applying the wrong fix, wastes precious minutes during a live incident.
The mapping breaks down like this:
- Layer 3 (network): Volumetric floods like UDP floods, ICMP floods, and amplification attacks that saturate your uplink with raw traffic. Symptom: a sudden bandwidth spike, often measured in gigabits per second, with your VPS unreachable even though CPU load looks normal.
- Layer 4 (transport): SYN floods, ACK floods, and connection-state exhaustion attacks that fill your server’s connection table. Symptom: a growing SYN_RECV backlog in
netstatorssoutput, climbing conntrack usage, and a server that feels “stuck” without heavy bandwidth use. - Layer 7 (application): HTTP floods, slow-read attacks, and API abuse that mimic legitimate requests. Symptom: high CPU or memory load on the application process with bandwidth that looks entirely normal, because the requests are small but expensive to process.
This layer mapping matters because it tells you who has to fix the problem. On-VPS tuning and firewall rules can blunt L4 and L7 issues, but a true volumetric L3 flood, anything measured in double-digit gigabits per second, exceeds what a single network interface can absorb. At that point, only the provider’s edge scrubbing or blackhole routing can help. If your bandwidth graph is pinned flat while your VPS is unreachable, that’s your signal to escalate to the host immediately rather than tweaking iptables rules that will do nothing against a flood upstream of your network card.
How Do Providers Actually Mitigate DDoS Attacks?
Providers lean on two fundamentally different responses, and the difference between them decides whether your server survives an attack or simply disappears from the internet until it’s over.
Null-routing (also called blackholing) is the blunt instrument. When inbound traffic to your IP crosses a threshold, commonly somewhere between 1 and 20 Gbps depending on the provider, the network drops all traffic to that address, legitimate and malicious alike. Your VPS goes dark, usually for anywhere from a few minutes to several hours, until the attack subsides. It’s cheap for the provider to run and it protects their shared infrastructure, but it does nothing for your uptime. Most VPS hosts default to this because scrubbing at scale costs real money to operate.
Scrubbing centers take the harder route: they redirect your traffic through dedicated infrastructure that inspects every packet, drops the malicious portion, and forwards clean traffic back to your server. This can run in routed/BGP mode, where the provider announces your IP block through their scrubbing network at the routing level, or proxy mode, where a load balancer or reverse proxy sits in front of your origin and only ever exposes the proxy’s IP to the internet. Proxy mode also hides your real server address, which cuts off a large class of direct-to-origin attacks before they start. Fortinet’s rundown of mitigation techniques covers rerouting, sinkholing, and behavior-based bot detection as the standard toolkit scrubbing providers combine.
Before you sign up with any host, ask these questions directly:
- What’s your null-routing threshold, and how long is a typical blackhole held before traffic is restored?
- Do you offer scrubbing, and is it automatic or does it require a support ticket?
- Can I get per-VPS traffic reports or PCAPs after an incident, for forensics?
- What’s your SLA for first response during an active attack?
Pro Tip: Ask specifically what happens to your VPS during an attack, not just whether “DDoS protection” is included. Marketing language rarely distinguishes between a five-minute null-route and real-time scrubbing, and the operational difference between those two is the whole ballgame.
What VPS Settings Reduce DDoS Damage at the Network Level?
Your VPS has hard resource ceilings, a fixed vCPU allocation, a capped number of network interrupts per second, and a finite conntrack table, and none of that changes no matter how well you tune the kernel. That’s why on-host hardening is about buying time and reducing collateral damage, not stopping a volumetric flood outright.
Start with these kernel and firewall adjustments:
- Enable SYN cookies. Set
net.ipv4.tcp_syncookies = 1in/etc/sysctl.confso the kernel can validate connections without holding state for every half-open SYN request, neutralizing basic SYN floods. - Size your conntrack table for headroom. Raise
net.netfilter.nf_conntrack_maxwell above default (often 65536) and monitorconntrack -Cso a connection flood doesn’t silently exhaust the table and drop legitimate traffic. - Tune the SYN backlog. Increase
net.ipv4.tcp_max_syn_backlogto give the kernel more room to queue legitimate handshakes during a moderate spike. - Drop invalid packets at the firewall. With
nftables, a rule likeadd rule inet filter input ct state invalid dropclears out malformed and out-of-state packets before they consume conntrack slots. - Rate limit by connection rate, not just by IP. An
nftablesrule limiting new connections per source (limit rate 20/second) slows down basic flooders without blocking real users on shared NAT. - Whitelist UDP ports explicitly. Most VPS workloads don’t need open UDP at all; closing it removes an entire class of amplification vectors.
The kernel’s own sysctl documentation is worth bookmarking, since these parameters shift slightly across kernel versions.
For observation, iftop and vnstat show real-time and historical bandwidth by connection, while ss -s gives you a fast summary of socket states across the box. A baseline iperf test run during quiet hours tells you what “normal” throughput actually looks like, so a spike is obvious instead of guesswork. Watch for one figure specifically: a sustained jump in packets per second with average packet size dropping, which is the classic fingerprint of a small-packet flood designed to exhaust CPU interrupt handling rather than bandwidth.
How Do You Stop Layer 7 DDoS Attacks on a VPS?
Layer 7 floods are the hardest category to catch at the network level because the traffic looks like real visitors, just far too many of them, or a handful of visitors making far too many requests. The fix lives at the application boundary, not the firewall.
Put a CDN and managed WAF in front of your origin. This absorbs a large share of request-per-second floods before they ever reach your VPS, challenges suspicious clients with bot-detection logic, and applies managed rule sets tuned against known attack signatures. Cloudflare’s documentation on multi-layer protection describes how anycast routing and behavior-based filtering work together across L3 through L7, and IBM’s overview of WAF mechanics explains why a WAF catches malicious application requests that a standard port firewall simply can’t see.
Behind the CDN, configure your reverse proxy to do real work instead of just passing traffic through:
- Rate limit by URI path in NGINX or HAProxy, so
/loginand/api/endpoints get far stricter limits than static asset paths. - Cap concurrent connections per client IP to stop a small pool of attacking hosts from monopolizing worker processes.
- Set aggressive timeouts for slow-read and slow-POST connections that try to tie up threads indefinitely.
Cache everything cacheable. Static assets should never touch your application server during an attack, and even dynamic pages often tolerate a short cache window (30 to 60 seconds) that dramatically cuts backend load during a request flood. Treat login forms and API endpoints as a separate budget with their own, tighter rate limits, since those are the routes attackers target specifically because they’re expensive to process.
Finally, shield your origin. Lock your firewall to only accept traffic from your CDN or proxy provider’s published IP ranges, and make sure no DNS record anywhere still points directly at your VPS’s real IP.
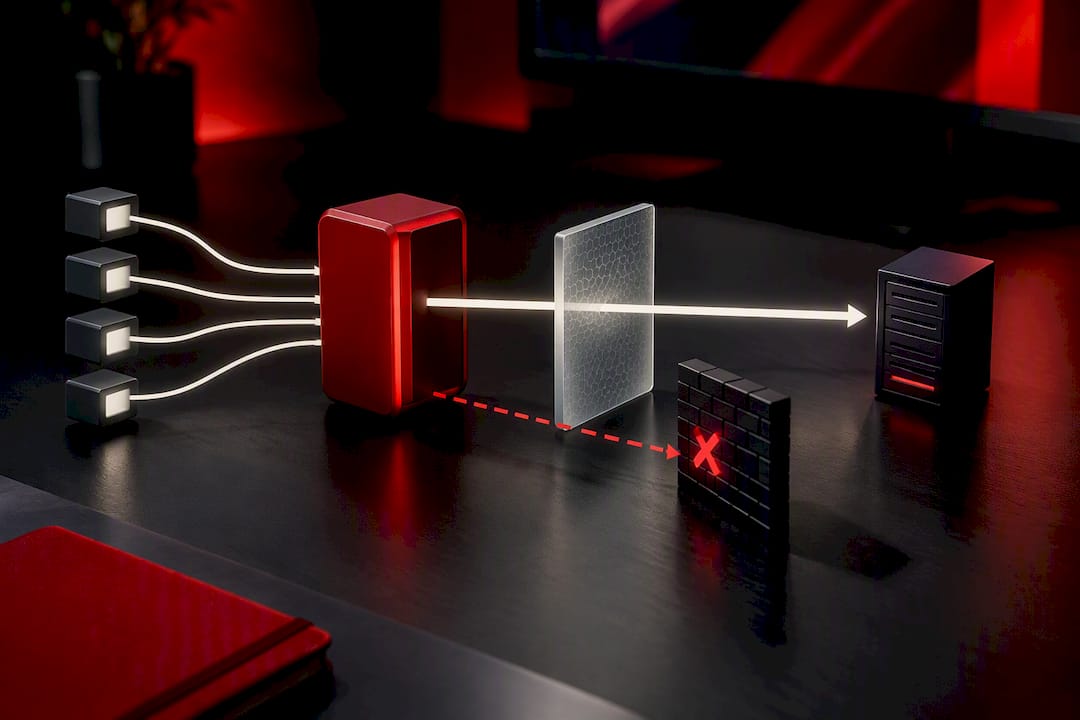
Pro Tip: Run a DNS history check on your own domain before an attack happens. An old A record pointing straight to your origin, left over from before you added a CDN, hands attackers a direct path around every edge protection you’ve built.
How Should You Monitor and Respond to a DDoS Attack?
A rehearsed playbook beats improvisation every time, because DDoS incidents move faster than a team can debate options in a chat thread. Kentik’s guidance on DDoS programs makes the point bluntly: waiting for a decision meeting during an active attack is how mitigation fails.
Collect this telemetry continuously, not just when something breaks:
- Flow data (NetFlow or sFlow) from your router or provider dashboard, showing traffic by source and port.
- Interface counters for bandwidth and packets per second, tracked against your established baseline.
- WAF and reverse proxy logs, filterable by URI and response code.
- BGP session state if you run your own announcements or use routed-mode scrubbing.
Pre-configure automated triggers instead of manual ones wherever your provider supports it. Threshold-based alerting, FlowSpec rules, and Remote Triggered Black Hole (RTBH) policies can kick in within seconds of an anomaly, long before a human notices a dashboard turning red. A tool like Opsphere’s operational monitoring approach illustrates how teams wire flow telemetry into automated alerting so detection doesn’t depend on someone staring at a graph at 3 a.m.
When you do escalate to a provider, send them exactly what they need on the first message:
- Precise start time of the anomaly, down to the minute.
- Peak bandwidth (bps) and packet rate (pps) observed.
- Affected ports and protocols.
- Your own IP and any error messages from your monitoring stack.
After the dust settles, request forensic artifacts: PCAPs and a per-VPS incident report, per Flowtriq’s breakdown of what premium providers actually deliver. Use them to tune your thresholds before the next attempt.
What Should You Do the Moment Your VPS Comes Under Attack?
- Check your bandwidth graph and connection states immediately; note the exact timestamp the anomaly started.
- Pull logs from your firewall, reverse proxy, and application, and save them somewhere off the affected VPS.
- Enable SYN cookies and tighten rate limits if they weren’t already active.
- Apply emergency firewall rules to drop invalid packets and cap new connections per source.
- Trigger provider-side mitigation if you have it, or open a support ticket with your bandwidth and pps figures ready.
- Expect a null-route if you’re on a standard plan; expect continued (degraded) service if you’re on scrubbing.
- Once traffic normalizes, rotate any exposed API keys or credentials that may have been probed during the noise.
- Review your logs for the actual attack vector and update your playbook and firewall rules accordingly.
CISA’s guidance on responding to denial-of-service incidents covers the same sequence at the enterprise level, and it holds up just as well for a single VPS.
How AceRDP Approaches Layered DDoS Protection
A VPS provider’s job in this whole model is to own the two hardest layers: raw edge capacity and the hardware headroom to keep working while under partial load. AceRDP runs on modern AMD Ryzen infrastructure with NVMe storage and low latency, which matters directly during an L7 event, since a CPU-bound request flood degrades a server far less when there’s real headroom to absorb the extra processing load.
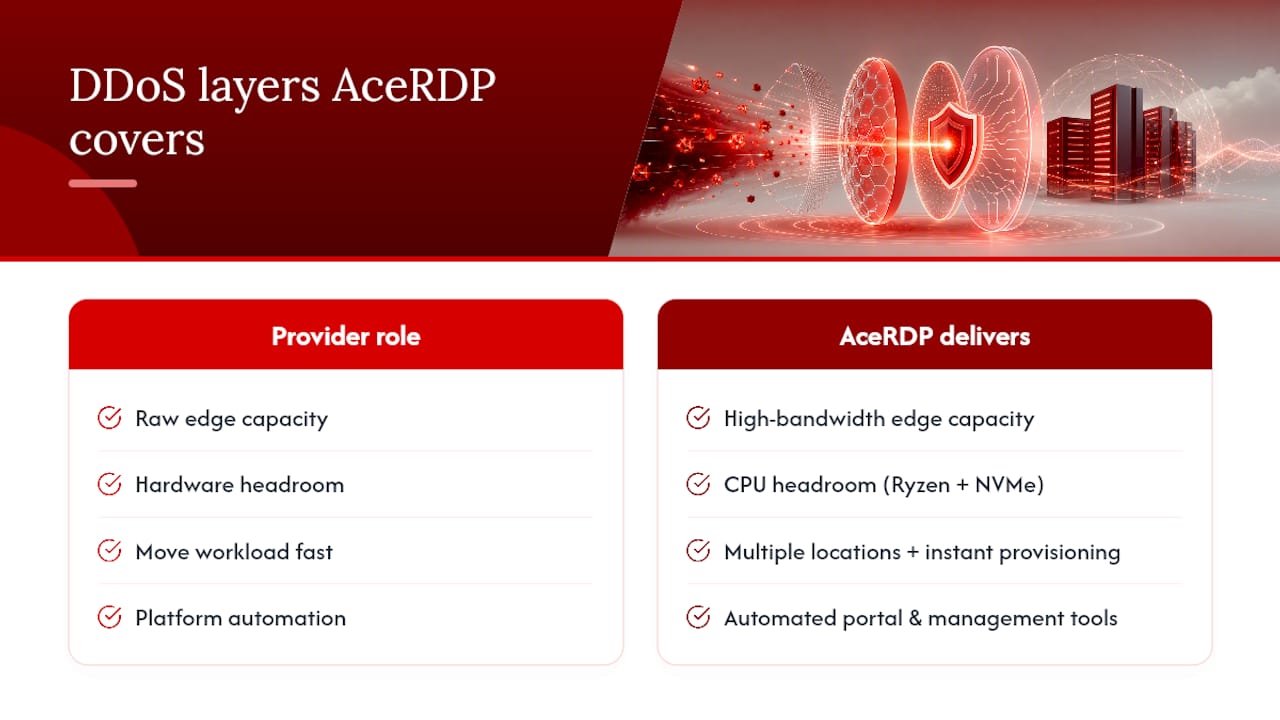
On the platform side, AceRDP customers deploy and manage Windows or Linux servers through an automated portal that includes multiple hosting locations, DDoS protection, instant provisioning, and built-in server management tools, all without waiting on a manual setup process. That combination lets you spin up a replacement instance in a different location quickly if you ever need to shift workload during a sustained attack rather than riding out a long blackhole in one spot.
The broader positioning is straightforward: strong CPU performance and DDoS protection at prices built for the demanding side of VPS use, remote desktop workloads, automation pipelines, and development environments where downtime has a real cost.
— AceRDP
When Does Null-Routing Make Sense Versus Paying for Scrubbing?
Null-routing is fine for low-stakes workloads: a dev sandbox, an internal tool, a personal project where a few minutes or hours of downtime costs nothing real. It’s the wrong tradeoff the moment your VPS runs anything customer-facing or revenue-generating.
For small businesses, the practical minimum is a provider with at least basic scrubbing or a CDN in front of the origin, paired with the on-VPS hardening covered above. That combination handles the majority of opportunistic attacks without a five-figure security budget.
Technical operators running anything mission-critical should go further: per-VPS telemetry, a written and rehearsed incident playbook, and a provider relationship where you already know their escalation contact before you ever need it. Budget for scrubbing capacity as insurance, not an afterthought purchased mid-incident.
Get DDoS-Protected VPS Hosting Built for Performance
Every layer covered above, edge mitigation, kernel tuning, WAF rules, and a rehearsed playbook, only works if the underlying server has the CPU headroom to keep functioning while it’s under partial load. AceRDP is built around that requirement: AMD Ryzen hardware for real processing power, DDoS protection baked into every plan, and multiple hosting locations so you’re not stuck rebuilding from scratch if you need to shift a workload.
Before you commit to any provider, get the specifics in writing: their null-route threshold, whether scrubbing is included or an add-on, and whether you can request a per-VPS report after an incident. Those details separate a marketing checkbox from an actual defense layer.
AceRDP offers multiple VPS plans at various price points, including options priced monthly and one-off, to suit different customer needs. Review the full lineup of VPS plans and match your workload, remote desktop, development, or automation, to the CPU and storage tier that fits, then provision your server and get your DDoS terms confirmed before you ever need them.
Sources
- DDoS Protected VPS Hosting: What It Actually Means in 2026 | Flowtriq Blog
- How DDoS mitigation works | Fortinet
- Cloudflare DDoS protection docs
FAQ
What Are Layer 7 DDoS Attacks?
Layer 7 attacks target the application layer, flooding a server with HTTP requests, API calls, or slow connections designed to look like legitimate traffic. They’re hard to catch with a firewall alone because bandwidth stays normal while CPU and memory load spikes, which is why WAF and reverse proxy rules matter more than network-level filtering for this layer.
Which Layer Does a DDoS Attack Target?
DDoS attacks can hit any of three layers: Layer 3 (network, volumetric floods), Layer 4 (transport, connection exhaustion like SYN floods), or Layer 7 (application, request floods). The specific layer determines the fix, since a firewall rule that stops a SYN flood does nothing against an HTTP flood.
What Is Layer 7 in the Context of Cybercrime?
In cybersecurity, Layer 7 refers to the application layer of the OSI model, the part of the stack where actual user requests like web page loads and API calls get processed. Attackers targeting Layer 7 aim to exhaust application resources rather than network bandwidth, making these attacks harder to distinguish from real traffic without behavior-based detection.
Is Launching a DDoS Attack Illegal?
Yes. Launching a denial-of-service attack against systems you don’t own or have explicit authorization to test is illegal in most jurisdictions, and CISA treats it as a criminal cyber incident requiring formal reporting and response. If you’re a victim, document everything, bandwidth figures, timestamps, and affected ports, since that evidence matters for both provider escalation and any law enforcement report.
Does AceRDP Include DDoS Protection on Its VPS Plans?
AceRDP includes DDoS protection across its VPS hosting plans, alongside modern hardware and multi-location deployment options. Exact plan pricing, from Bronze at €15 per month up to Legend at €100 per month, is listed on the AceRDP plans page, where you can also confirm DDoS-specific terms before ordering.